Learn about data storage and transfer
Last updated: November 9, 2026
This guide covers the essential aspects of data storage and transfer at Fireflies, including storage locations, compliance, and security practices.
Data storage
1. Storage locations
Public cloud: By default, your data is stored and processed in Fireflies' secure cloud infrastructure in the United States (AWS and GCP).
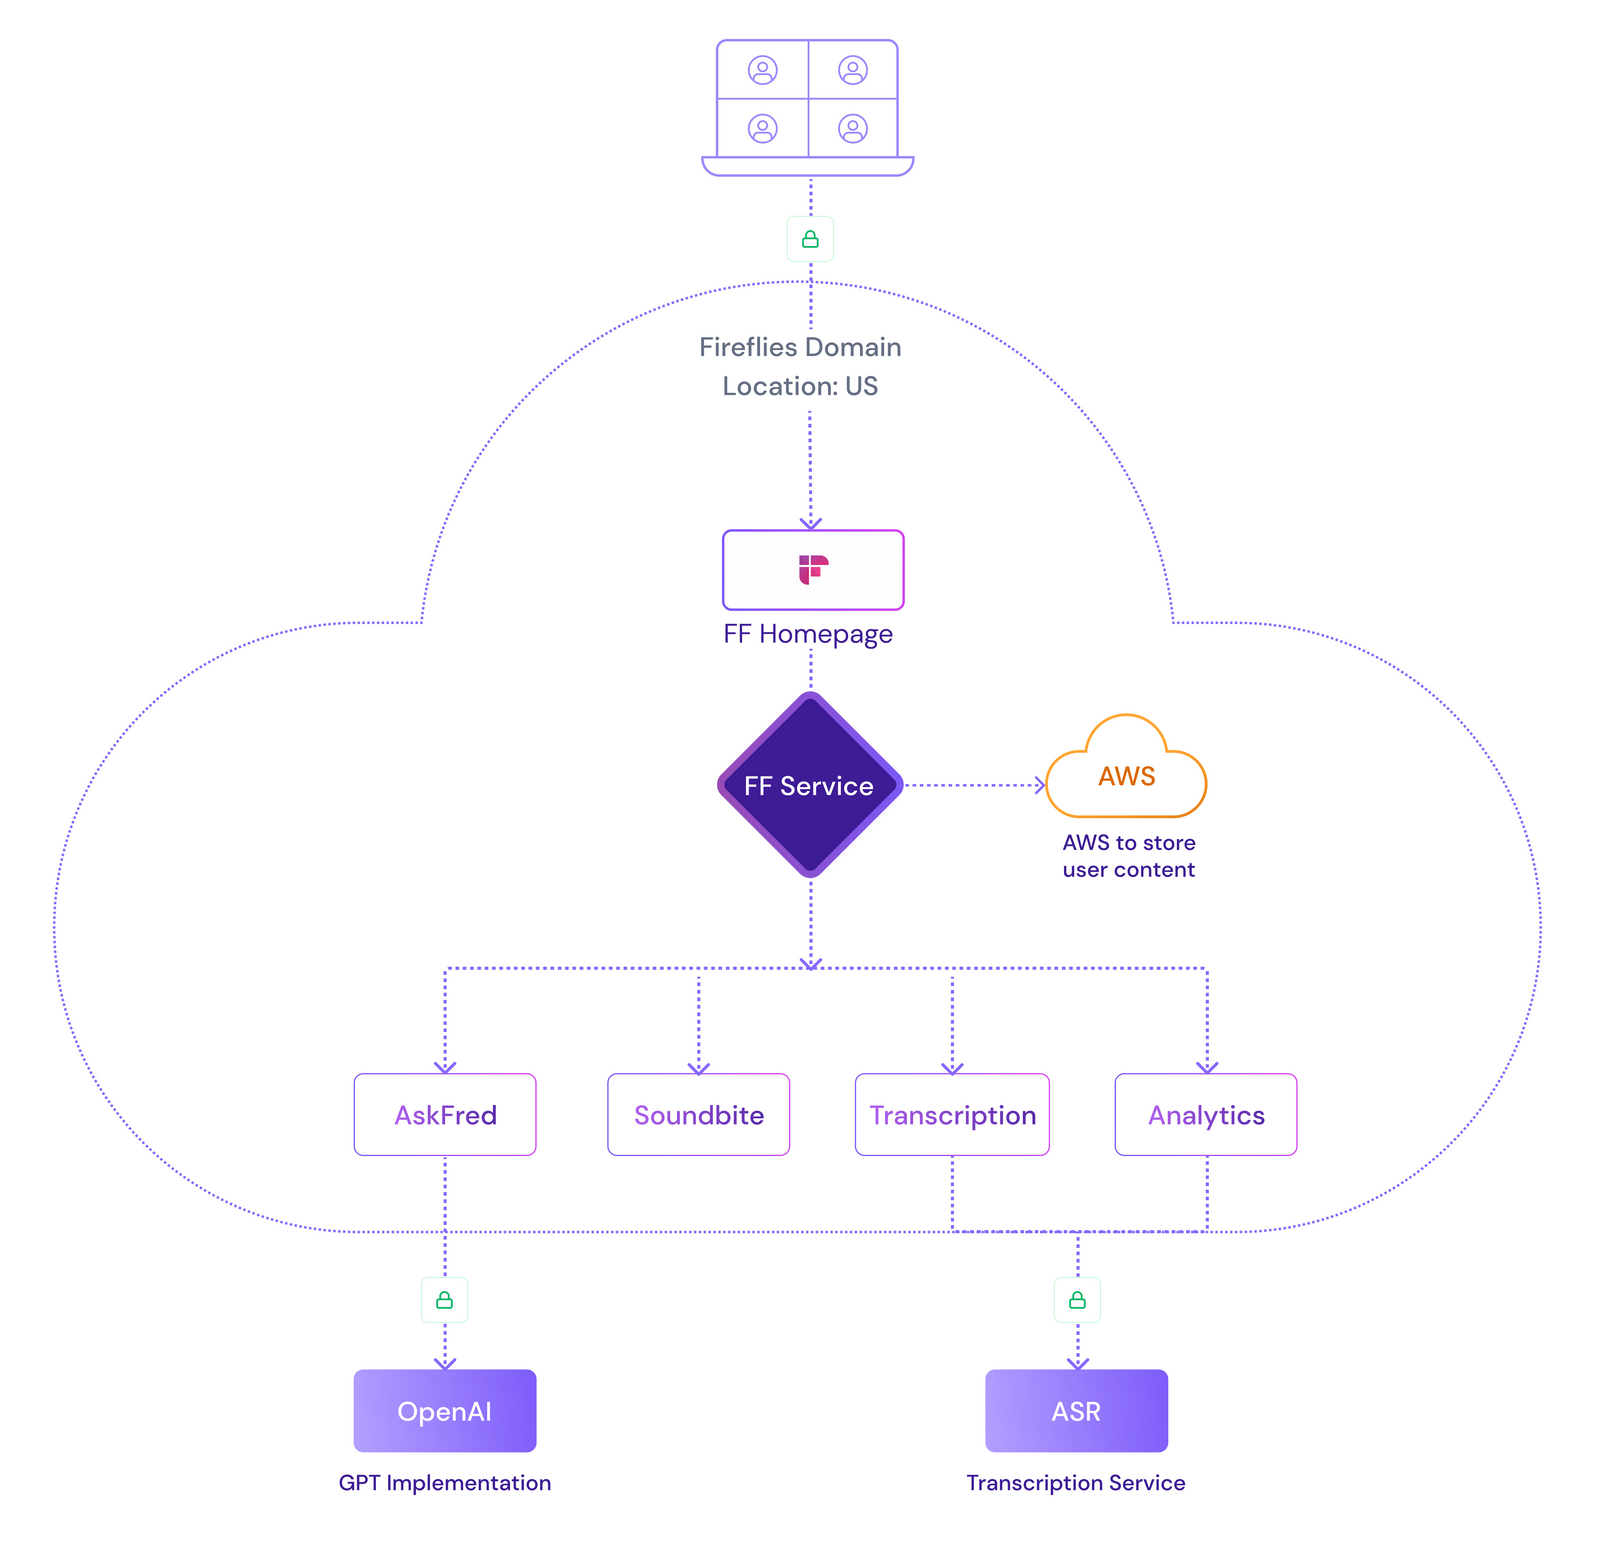
Private storage:
Fireflies offers private storage for organizations dealing with sensitive data or stringent compliance needs. (Available in the Enterprise plan).
With Private storage, you can store your meeting data in a dedicated and isolated storage. Bring Your Own Storage (BYOS) on AWS S3 or Google Cloud Storage.
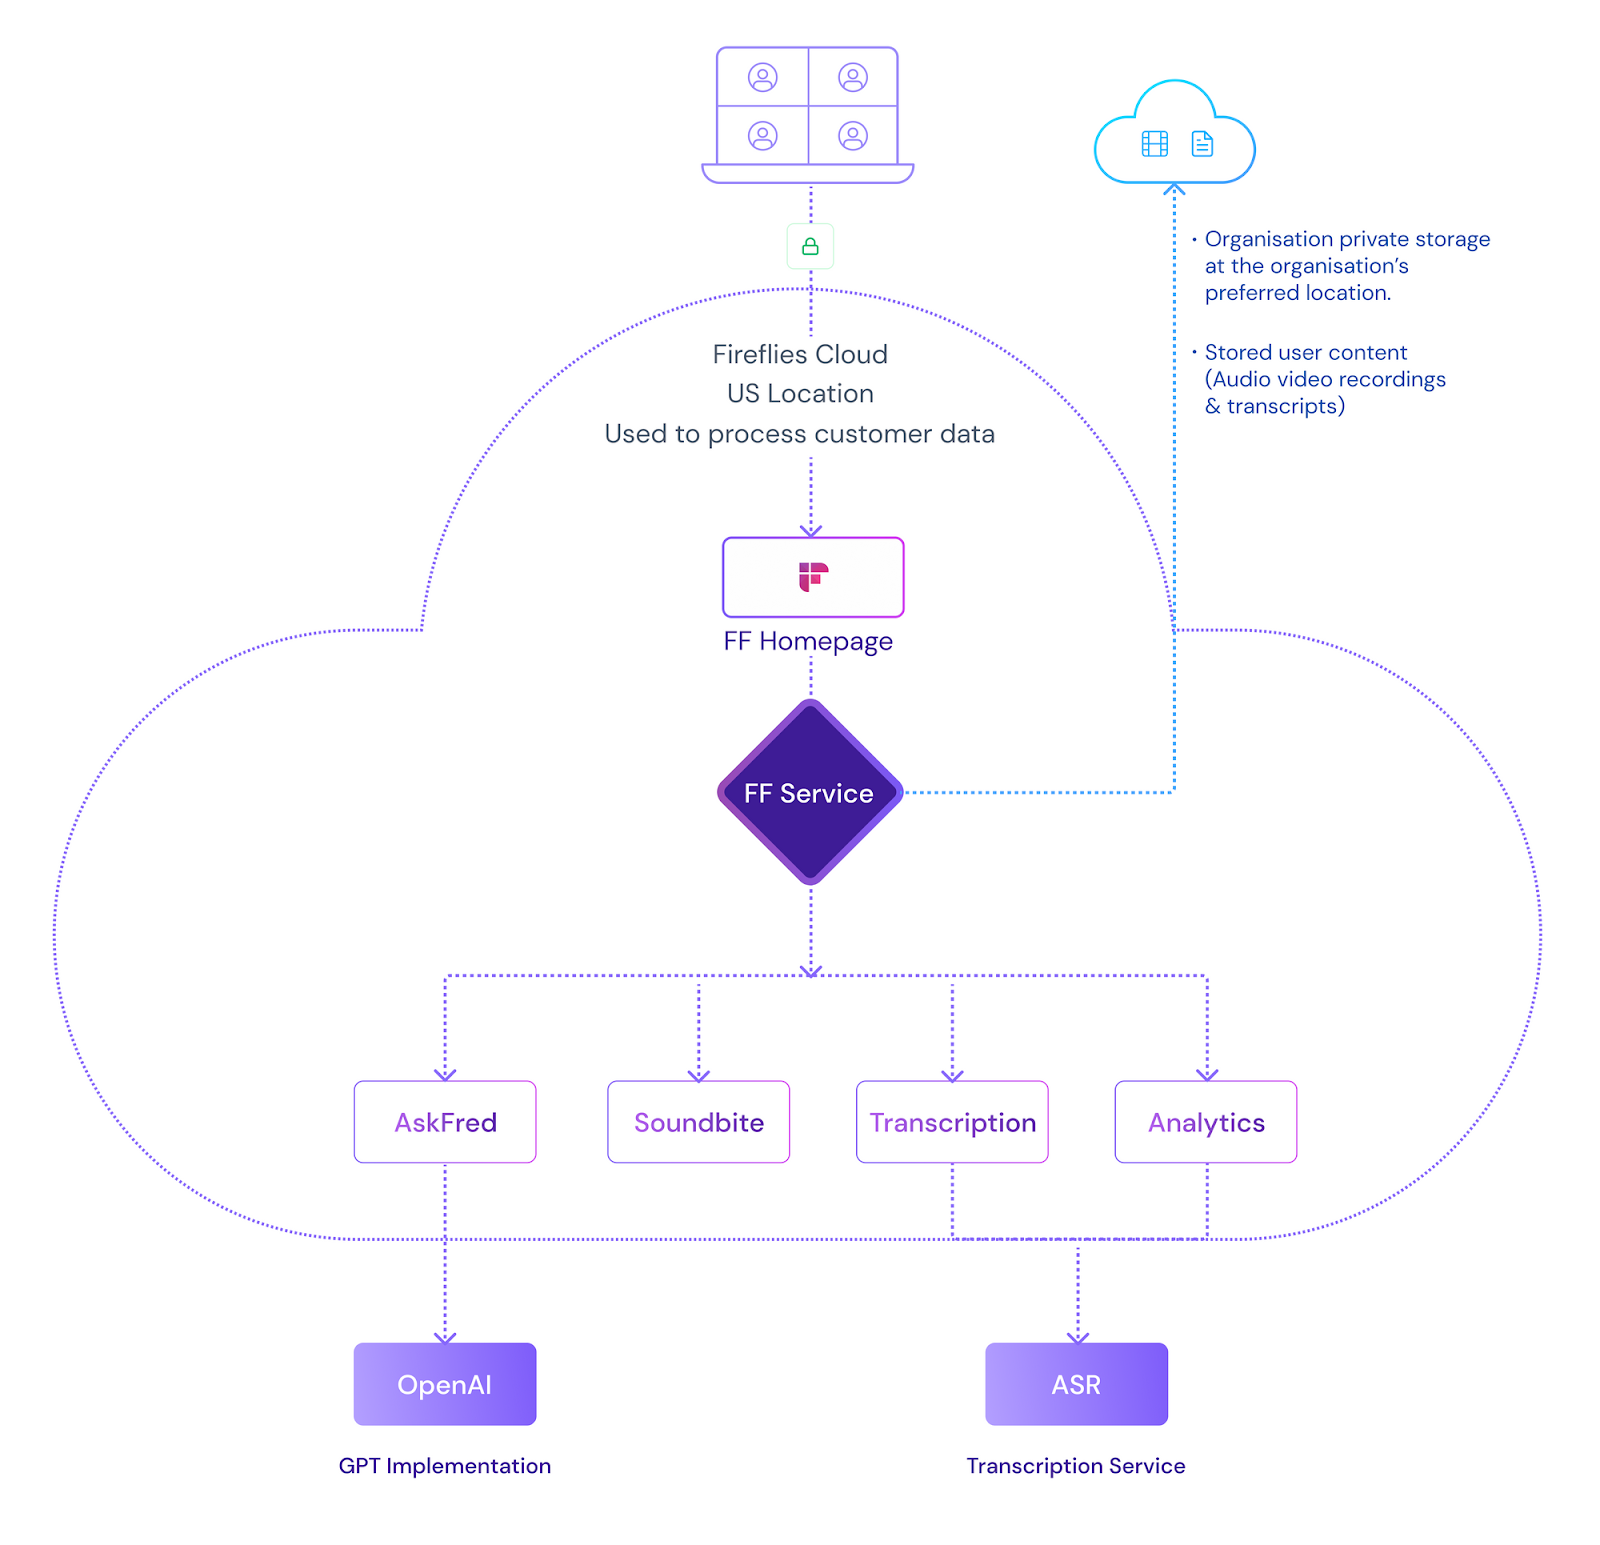
Note:
Your data will be stored in the EU, but processed in the US.
Related: Fireflies Private Storage
2. Data encryption
All user data, including transcripts, recordings, calendar events, emails, and settings, is encrypted end-to-end using 256-bit AES encryption for data at rest and TLS 1.2 encryption for data in transit.
3. Data ownership
You have complete ownership of all your data, as stated in the Fireflies Terms of Service.
Fireflies does not use your data to train AI models. Fireflies doesn’t sell your meeting data. We share it only with the service providers listed on our subprocessor page, under contract, to run the service.
4. Data type collected
We collect and store user content and user metadata.
User content: Transcription, Summaries, Audio and video recordings, AskFred chats, Soundbites, and any derivatives of such.
User metadata: Calendar metadata, meeting participants' emails and names, usage logs, and user settings/configuration.
Data transfer
Data backups and disaster recovery
All user data, including meeting transcripts, audio recordings, calendar events, emails, and user settings, is encrypted using industry-standard 256-bit AES encryption both at rest and in transit.
Related: Learn about how we encrypt your data
Data privacy and compliance
1. Compliance
Fireflies is SOC 2 Type 2 and GDPR compliant, and HIPAA-ready on Enterprise plans with Private Storage and a signed Business Associate Agreement.
Fireflies is ISO/IEC 42001 certified for responsible AI governance.
Fireflies also supports FERPA requirements for safeguarding student education records at educational institutions.
Fireflies is listed in the EU-US Data Privacy Framework, ensuring adherence to data protection requirements for EU residents.
2. Data privacy
Our AI vendors are contractually barred from training models on your data. See the subprocessor list at trust.fireflies.ai/subprocessors.
For educational institutions, Fireflies also offers a Data Sharing Agreement (DSA) to support FERPA compliance when handling student education records.
We follow the principle of least privilege, strictly granting access to sensitive data on a need-to-know basis, with monitoring and auditing.
If greater access is needed, for example, during a support request, you must first grant your permission.
Related: Policy on keeping information safe.
Security practices
Fireflies regularly scans for vulnerabilities and has an ongoing bug bounty program to detect and address security issues.
In case of a security breach, Fireflies will investigate, notify affected individuals, and take appropriate steps as per applicable laws and regulations.
Related: Fireflies Security FAQs